



Author: Nancy, PANews
The world is entering an era of asymmetric warfare.
On the physical battlefield between the US and Iran, Iran is waging a war of attrition through low-cost drones, missiles, and maritime blockades, tying down American military resources at relatively limited cost while applying pressure to the global economy.
In the crypto world, AI is lowering the technical barrier to cyberattacks and amplifying attackers' operational efficiency and destructive capability. Attackers may need only limited resources to inflict enormous damage on large enterprises and complex systems.
$11.8 Billion: A State-Level Hacker Army
North Korean hackers launch attacks with alarming frequency, keeping the crypto market on edge. Some are busy fortifying their security defenses, while others are taking a different approach. A developer recently designed a rather unconventional verification mechanism aimed at stopping North Korean users from accessing a website on a psychological level. Unexpectedly, this security experiment—half tongue-in-cheek—attracted a real cyberattack.
From a frequent keyword in security incidents to fodder for memes in the crypto community, North Korean hackers are becoming an inescapable topic in the industry. And behind the jokes lies the market's growing anxiety about cybersecurity risks.
Chainalysis data shows that as of October 29, 2026, losses from hacker attacks suspected to be linked to North Korea accounted for nearly 89% of the crypto hacking losses reported this year, up from 15% in 2021. In terms of losses per attack, the average loss from suspected North Korea-related attacks has risen from $50.65 million in 2021 to approximately $185 million in 2026—about 3.7 times the 2021 figure.
As one of the countries under long-term international sanctions, North Korea finds it difficult to obtain foreign exchange and resources through normal international trade and financial activities. Cyberattacks have therefore gradually become an important means for it to acquire funds and circumvent financial restrictions.
North Korea's hacking force is not a group of skilled technicians each fighting alone, but a highly organized state-level cyber operations system built over many years. From talent selection and elite education to militarized training, and then to overseas infiltration and real-world operations, North Korea has established a relatively complete talent cultivation and operational mechanism.
This mechanism resembles the pyramid-style selection process for Olympiad competitors. A small number of teenagers with outstanding logical thinking and mathematical talent are identified nationwide, while their political background and loyalty are vetted. Those who pass the selection gain access to concentrated educational resources and receive long-term, systematic training in computer science, mathematics, and programming.
After completing domestic training, some personnel are dispatched overseas to operate as students, IT practitioners, or remote technical workers, accumulating technical experience in real environments while learning the language, culture, and work habits of target countries in preparation for future operations.
To attract and retain these technical talents, North Korea also offers special privileges, including exemption from certain military service obligations, residency rights in the capital, housing, higher incomes, and better education and healthcare resources. For a country with limited resources, these incentives are considerably attractive. Hackers with scarce technical skills thus acquire special social status and gradually become a new privileged class within North Korea.
Talent cultivation is only the first step. Highly specialized organizational division of labor is the real trump card of North Korea's "keyboard warriors." Reconnaissance personnel are responsible for gathering global cyber intelligence and identifying system vulnerabilities to select targets for attack operations; operatives use identity disguise, social engineering, and malware to carry out infiltration and steal funds and sensitive information; and there are dedicated personnel responsible for fund transfers, money laundering, and asset liquidation, converting cyberattack proceeds into disposable funds.
From target selection and technical infiltration to fund transfer, what appears to be a simple crypto asset theft may behind it involve a complete cross-border operational chain. Lazarus Group, APT38, Kimsuky, and others are distinct North Korea-linked hacking organizations identified by external security agencies based on their attack targets, technical methods, and behavioral characteristics.
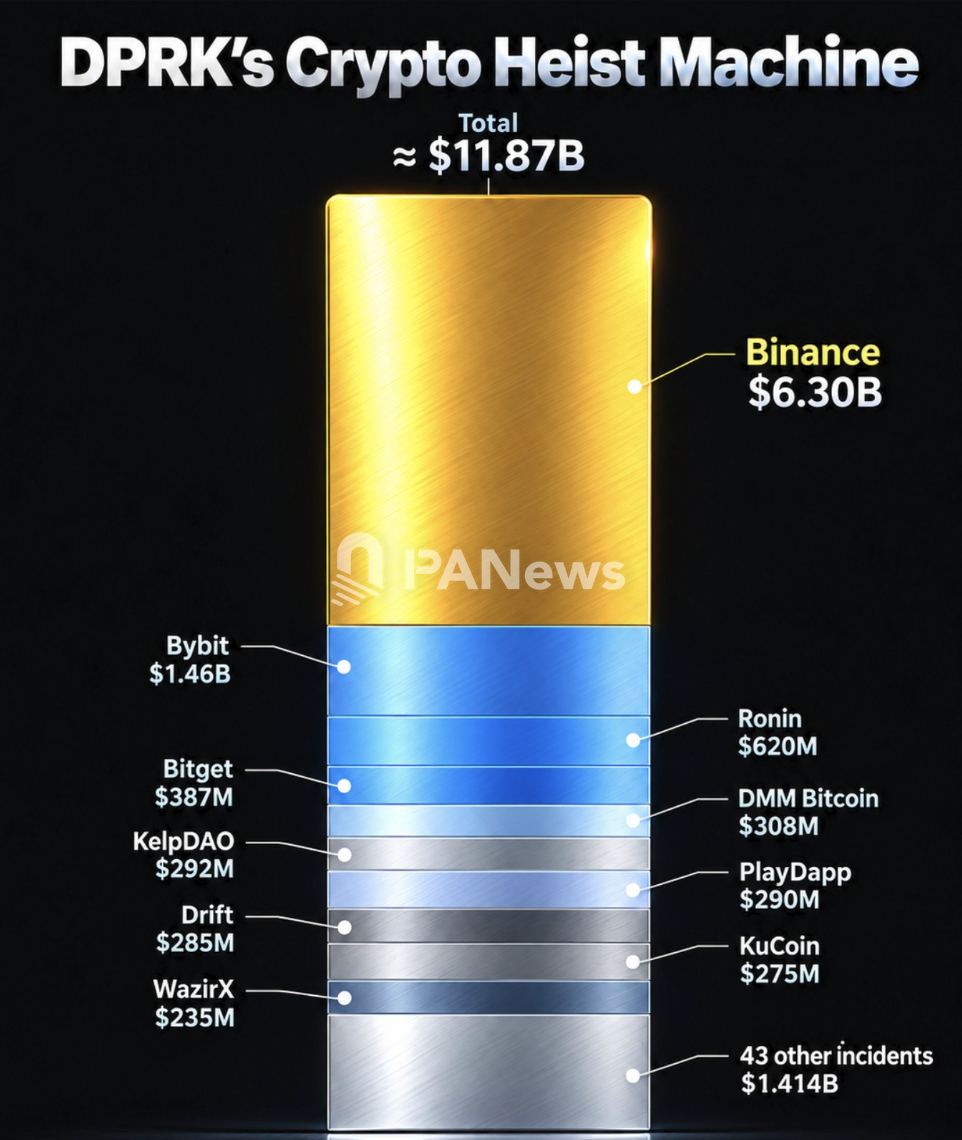
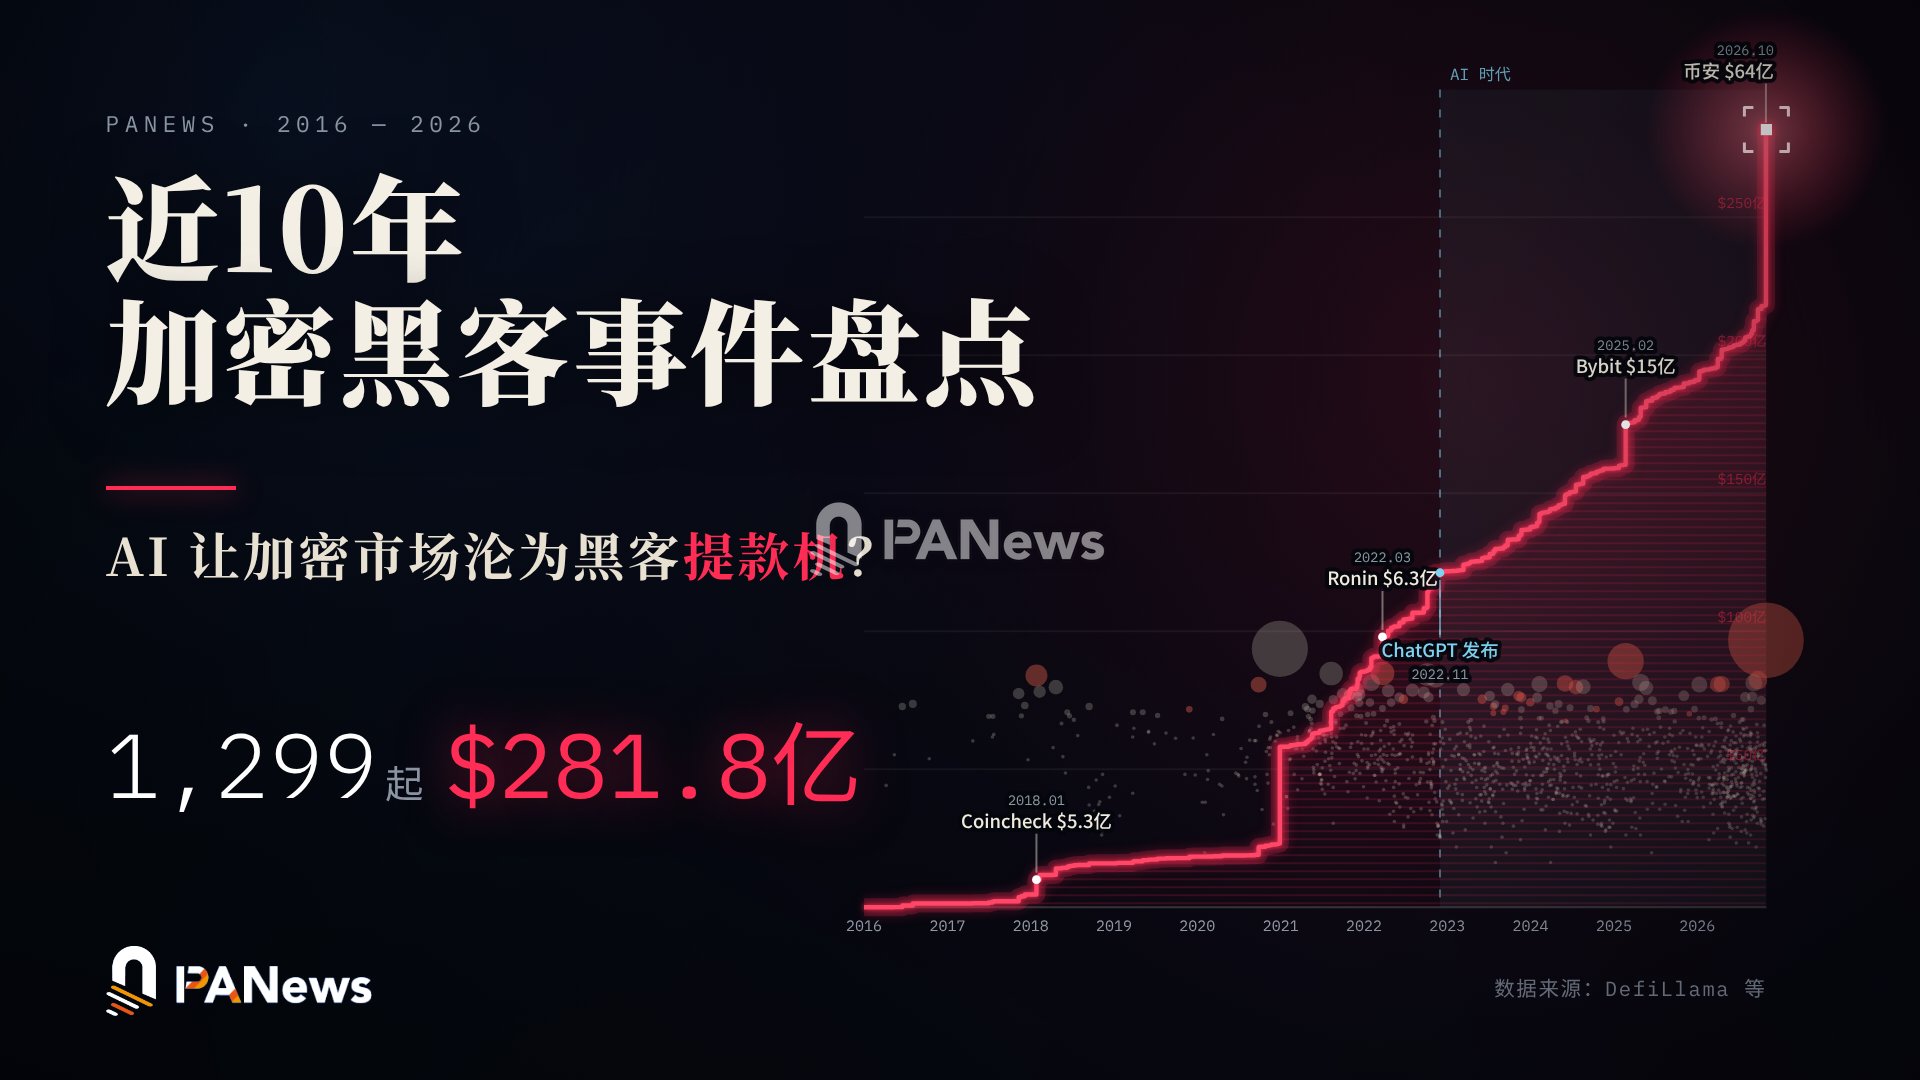
According to recent disclosures by analyst Darkfost, following the attack on Binance, the total funds stolen by the Lazarus organization have reached $11.87 billion. According to 2025 data from the Bank of Korea, this figure is equivalent to 45% of North Korea's GDP and 35% of its Gross National Income (GNI). If this estimate holds, cyberattack proceeds are no longer merely additional illicit income but could become a considerable source of funding within North Korea's economic system.
For North Korea, cyberattacks are both a strategic weapon and another channel for bypassing financial blockades and acquiring economic resources. A country that the traditional financial system can hardly reach is using cyberspace to find new ways of acquiring resources.
The Biggest Security Vulnerability May Be the "Colleague" Next to You
When attackers no longer attempt to breach firewalls head-on but instead seek entry points from within the organization, the cost of attack is often lower and the stealth is greater. Traditional defense systems built on security appliances and network perimeters are facing new challenges.
North Korean hackers are taking this asymmetric approach to its extreme. Through carefully fabricated resumes, forged passports and identity information, they pose as IT practitioners or job seekers and proactively approach core employees such as developers and operations personnel at enterprises.
To further lower the other party's guard, attackers even participate in live video interviews and provide fake social media accounts containing lifestyle photos and daily updates, shaping as convincing a job-seeker image as possible. Once they pass the recruitment process and join a team, they can use their legitimate employee status to lie low for extended periods, gradually gaining access to internal systems, code repositories, and sensitive permissions, and seeking opportunities for further infiltration.
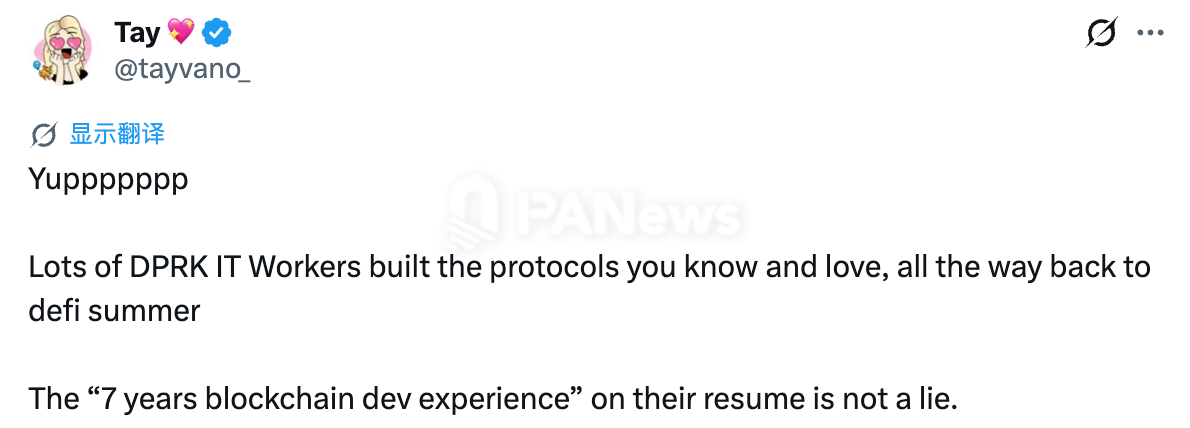
Ketman, a project funded by the Ethereum Foundation, once identified 100 North Korean IT personnel embedded in Web3 organizations over a six-month period. MetaMask security researcher Taylor Monahan previously disclosed that at least 40 DeFi protocols have employed North Korean IT personnel at some point during their development, spanning seven years. These individuals gained entry into Web3 teams through forged passports, visas, and carefully crafted resumes. What is more misleading is that some of their blockchain development experience is genuine.
According to Binance's latest disclosure, since the beginning of this year the platform has intercepted 57 cyberattacks suspected to be North Korea-related. Attack methods include infiltration through fake job interviews, malware disguised as commonly used developer tools, tampered software packages and browser extensions, and fake video conferencing applications used to trick employees into running malicious programs, as well as social engineering attacks to steal credentials and implant remote access trojans.
In the recent Binance incident involving over $6 billion in stolen funds, according to the investigation information initially disclosed by officials, attackers approached a software engineer on Binance's wallet infrastructure team through a fake high-salary recruitment offer. After multiple rounds of video interviews, the attackers induced the engineer to run a malicious program disguised as a technical test project on their work computer, ultimately gaining control of the employee's device and further threatening the security of the wallet infrastructure. SlowMist founder Yu Xian noted that such incidents constitute advanced persistent threats (APT), involving multiple stages including exploitation of human nature, intelligence reconnaissance, malware evasion, exploitation of trust chains, targeted lateral poisoning, cloud environment penetration, risk control bypass, and zero-day vulnerabilities.
Similar tactics have precedent. When Axie Infinity's Ronin Network was attacked in 2022, the North Korea-linked Lazarus Group also approached a senior engineer at Sky Mavis through LinkedIn with a high-salary position. After multiple rounds of interviews, the attackers sent a fake job offer file containing a trojan, ultimately gaining control of systems related to validator nodes and stealing approximately $625 million in assets.
This is precisely the asymmetric security dilemma facing the crypto industry. In the past, security defense relied more on building solid technical barriers; but as social engineering attacks continue to evolve, attackers do not necessarily need more advanced technology or more resources—they only need to find one weak link.
Compared with technical vulnerabilities, what is truly difficult to guard against may be the people who have already earned trust.
AI Escalates the Offense-Defense Battlefield: The Scramble for Resources Has Begun
If social engineering attacks lower the cost for hackers to breach organizational defenses, then the continuous iteration of AI further amplifies the scale and efficiency of cyberattacks.
The latest report from Microsoft's threat intelligence team shows that among the eight major North Korean hacking groups it tracks, three have deeply integrated AI tools into their daily attack workflows, reaching the highest level of Microsoft's AI application maturity model for cyber threats.
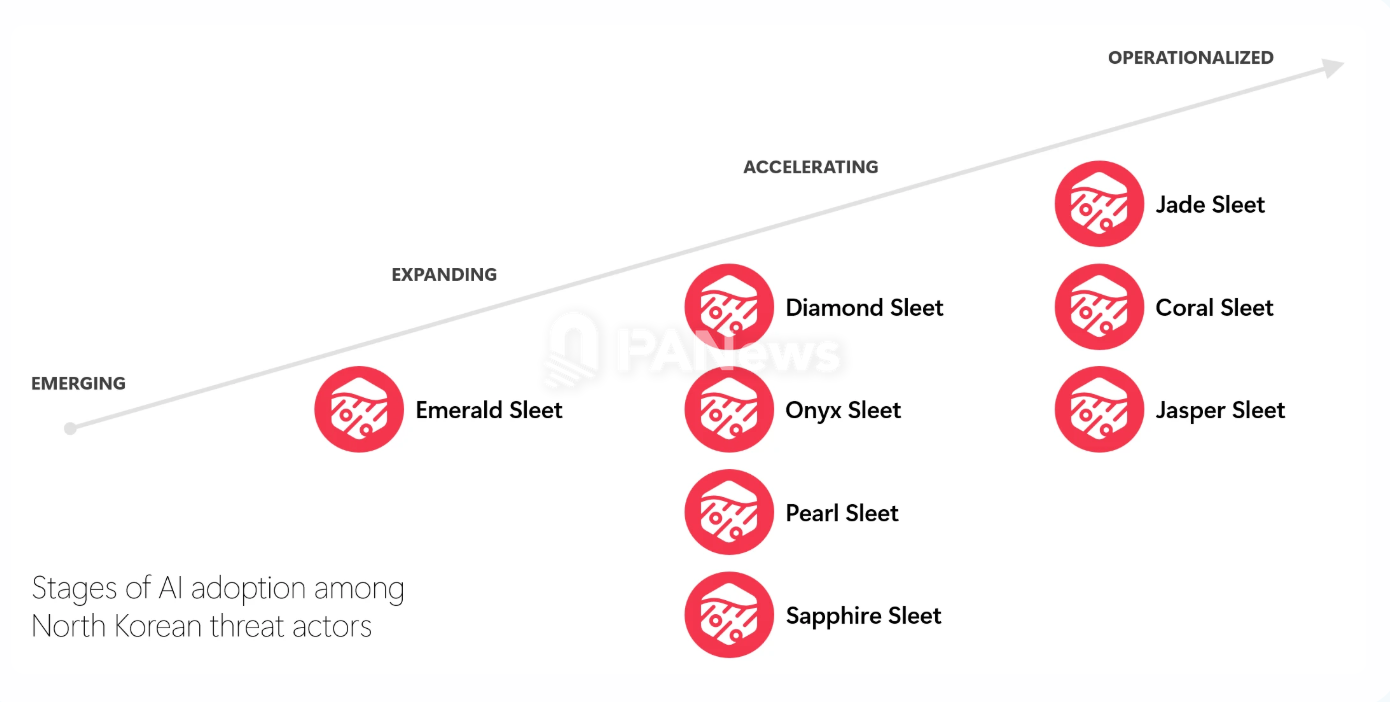
In social engineering and identity forgery, North Korean hacking groups use AI to mass-generate phishing, recruitment, and investment lure content, impersonate foreigners through translation and tone adjustment, and even generate fake resumes, interview answers, profile photos, and voice and video. One group generated more than 100 customized phishing PDF files targeting South Korean users between August and September 2026. North Korean remote IT personnel employed by overseas companies under false identities have also begun using AI to maintain multiple identities simultaneously.
According to South Korean security firm Genians, the North Korean hacking group Kimsuky had already set up a local large language model (LLM) and RAG environment by August of this year, leaving extensive records of using the AI code editor Cursor. When relevant tools were blocked, they quickly switched tools and continued their activities.
Microsoft believes these groups have not yet achieved fully autonomous attacks, and the actual impact of AI on attack success rates and costs remains unclear. But from target reconnaissance and social engineering to identity forgery and malware development, AI has already entered multiple stages of the attack chain. It may not directly turn an ordinary attacker into a top-tier hacker, but it can compress the time and manpower required to carry out complex attacks.
In the Binance hacking incident, AI tools also became part of the attack. According to investigation information, attackers used a supply chain attack to provide the engineer with a tampered AI programming tool. Even after the engineer discovered the anomaly and switched tools, their position information and the information of other members of the wallet infrastructure team had already been exposed. Subsequently, after gaining control of one engineer's computer, the attackers used Binance's internal AI tools to further compromise other employees' devices, ultimately obtaining signing control.
As AI capabilities continue to grow, the competition between cyber offense and defense is also extending from traditional technology and talent competition to the contest for data, models, and computing resources, further exacerbating the asymmetry of cyber offense and defense.
Recently, security researcher Jun Song shared that an anonymous black-hat organization had contacted him, hoping to commission him to use exploit data to conduct reinforcement learning post-training on open-weight models, and was willing to pay extremely high compensation. Jun Song said the other party claimed to possess attack data at a scale he had never seen before—so large that even if someone told him it was an undercover dataset from law enforcement, he would believe it. By comparison, a white-hat project he participated in used GLM-5.3 with less than 1% of the data volume the other party claimed to have, yet the model's performance already substantially exceeded frontier models.
In the AI offense-defense competition, high-quality, large-scale exploit data may become an important resource for training cybersecurity models. Whoever can obtain more data, stronger models, and more ample computing power may gain an advantage in future offense-defense competition.
If massive exploit data can be effectively converted into model capabilities, attackers may further improve the efficiency of vulnerability discovery and attack execution. Correspondingly, whether defenders can obtain sufficient data, models, and computing power will also affect their ability to identify and respond to emerging threats.
Coinbase disclosed in June that it had obtained access to Anthropic's frontier model Claude Mythos and was using it to strengthen crypto wallet and asset security defenses. By contrast, months later Binance still stated it had not obtained similar access. Differences in access to frontier models may further widen the capability gap between companies in vulnerability discovery, automated security auditing, and risk defense.
From Iran using low-cost weapons to tie down US military forces, to North Korean hackers accelerating attacks through identity disguise, social engineering, and AI tools, the battlefields are different, but both point to one reality: resource advantage no longer means absolute security. What is truly dangerous is responding to the threats of a new era with the mindset of the old one.