






Original | Odaily Planet Daily (@OdailyChina)
Author | Golem (@web3_golem)
Key Takeaway: In March 2026, Consensys (the parent company of MetaMask) inadvertently hired a North Korean hacker, who participated in developing MetaMask's core wallet code and fiat on-ramp/off-ramp features. This incident exposed serious security vulnerabilities in large crypto companies' hiring and third-party outsourcing vetting processes.
Key Elements:
a. Using the fake identity "Tyler Knapp" (GitHub: imyugioh), the North Korean hacker was hired as a consultant through a third-party HR vendor in March 2026, gaining access to MetaMask's core wallet code.
b. One month after joining, the hacker was identified and had their permissions revoked by Consensys' internal security team, with no user asset losses reported. However, Consensys has not disclosed how they confirmed the hacker's identity, and the hacker's GitHub account had already been publicly listed on the Lazarus Group blacklist since September 2025.
c. Taylor Monahan, MetaMask's security lead, had long warned about North Korean hackers infiltrating hiring processes. Affected projects include SushiSwap, THORChain, Ronin, and now MetaMask itself.
d. Social engineering attacks (e.g., infiltrating hiring pipelines, posing as job applicants) are the most effective and lucrative method for North Korean hackers due to low cost and high persistence, while identity verification for companies remains expensive.
e. Recent cases: In 2026, Drift Protocol lost approximately $285 million due to a fake hire; in 2024, DMM exchange lost about $308 million; and in 2022, the Ronin bridge was drained of approximately $620 million—all linked to North Korean hackers exploiting recruitment processes.
Last week, MetaMask celebrated its 10th birthday, only to be hit by a "security scandal" revealing that it had accidentally hired a North Korean hacker.
On July 17, according to internal Slack records from Consensys obtained by Drop Site News, a North Korean hacker using the fake identity "Tyler Knapp" (GitHub account imyugioh) was hired as a consultant on March 9, 2026, through a third-party HR vendor that Consensys had a long-term relationship with. Internal records show that this hacker was not assigned to peripheral tasks but had access to MetaMask's core wallet code and worked on developing the wallet's fiat on-ramp and off-ramp features.
Imagine if the hacker had tampered with MetaMask's fiat gateways—assets belonging to tens of millions of users would have been at risk. Fortunately, this disaster did not occur. One month after the hacker joined, Consensys' internal security team noticed something suspicious. After an investigation confirmed that Tyler Knapp was indeed a North Korean hacker, Consensys immediately revoked all internal access and contacted law enforcement.
Matt Corva, Consensys' general counsel, stated that after launching a company-wide investigation into Tyler Knapp, he ordered an immediate halt to all MetaMask product releases, pleaded with everyone to keep the matter confidential, and instructed them not to engage with the individual.
Although this security incident resulted in no loss of user assets or data, Matt Corva has never disclosed how they ultimately linked Tyler Knapp to a North Korean hacking group.
Has Consensys' Hiring Process Been Infiltrated?
The question arises: how did a North Korean hacker so easily bypass Consensys' background checks during hiring?
Matt Corva's explanation was, "We learned about 'Knapp' through an existing partnership with a reputable third-party service provider." But this hardly justifies Consensys' failure to conduct a thorough background check on the candidate. More absurdly, Consensys may not have even performed a basic screening of Tyler Knapp during the hiring process, as the hacker's North Korean ties were not deeply concealed—anyone asking an AI could have uncovered them.
According to DeFi researcher @Zun2025 on X, the North Korean hacker's GitHub account is imyugioh, and it had been publicly listed on the Lazarus Group blacklist since September 2025, with the real name Mauro Liu. (Odaily: Lazarus Group is North Korea's largest hacking organization; the 2025 theft of $1.5 billion from Bybit was also attributed to them.)
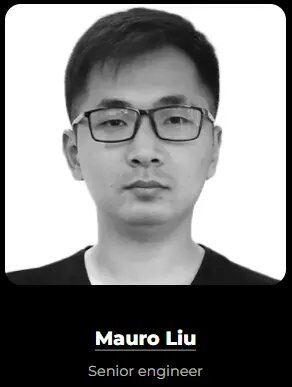
North Korean hacker imyugioh, real name Mauro Liu
Consensys' reluctance to reveal exactly how they identified Tyler Knapp as linked to North Korean hackers may stem from a fear of exposing vulnerabilities in their hiring process.
Matt Corva later defended the company, saying it had initiated a review of its practices for outsourcing engineering and development work. "We have reviewed all third-party services, including existing partnerships, to ensure that the strict standards applied to all employees are also applied to more complex third-party engagements," he said.
More ironically, Taylor Monahan, MetaMask's security lead, had been focusing on North Korean hackers infiltrating Web3 hiring processes for some time. She previously noted that North Korean IT experts have been actively participating in DeFi projects and contributing to well-known protocols. Their entry into DeFi/Web3 companies is not an isolated incident but has been ongoing for at least seven years. Affected projects have included SushiSwap, THORChain, Fantom, Shiba Inu, Yearn Finance, and Floki—and now MetaMask itself.
As a long-time observer of North Korean hackers, Taylor Monahan did not comment publicly on X about MetaMask's accidental hiring of one. While this incident constitutes "successful infiltration of the hiring process but not a successful attack," it still exposes MetaMask's overall security laxity, which starkly contrasts with its external image—allowing an outsourced contractor to access core code for a product module as critical as fiat on-ramp/off-ramp development.
Even large crypto companies like Consensys, despite having robust code auditing systems, are often more vulnerable than smaller teams when it comes to hiring and outsourcing vetting due to their size. The hiring process, in particular, is a weak point where hackers can more easily break through.
North Korean Hackers Posing as Employees Is Now the Easiest Way to Strike
Over the past year, with advances in AI and coding capabilities, many worry that hackers could exploit protocol vulnerabilities through AI to carry out attacks. Counterintuitively, however, historical data shows that for large companies, social engineering attacks are the easiest and most lucrative method for North Korean hackers.
Compared to launching external technical attacks, infiltrating hiring pipelines or posing as job applicants is cheaper for hacker groups. On-chain detective ZachXBT noted that many infiltration methods of the Lazarus Group, the largest North Korean hacking group, are surprisingly simple, such as posting job openings, connecting via LinkedIn, sending direct messages, and holding Zoom calls and interviews. This approach offers persistence and allows for "casting a wide net."
Additionally, this attack method exploits a cost asymmetry: North Korean hackers can create new identities almost for free, while for large crypto companies supporting remote work, third-party outsourcing, and open-source collaboration, continuous identity verification and vetting are costly and resource-intensive.
Many crypto companies have not been as fortunate as MetaMask in identifying an "insider" before a theft occurs.
In April 2026, North Korean hackers spent six months infiltrating Drift Protocol by gaining internal access through fake hiring or partnerships, resulting in a theft of approximately $285 million in user assets. In an earlier case from 2024, North Korean hackers entered the Bitcoin DMM exchange through hiring, accessed internal systems, and stole about $308 million. In 2022, a North Korean hacker posed as a blockchain game developer to join Ronin Network, eventually leading to the theft of approximately $620 million from the Ronin bridge—one of the largest crypto hacks in history at the time.
MetaMask narrowly escaped one incident but not a warning. For today's crypto industry, the biggest security risks may no longer lie in the code but outside of it. The security boundary of blockchain has long extended from on-chain to the real world. Code can be audited repeatedly, contracts can be upgraded continuously, but identity is difficult to verify. In the past, people often viewed smart contracts as the weakest link in crypto. Now, it seems the truly hard-to-defend elements are management processes—and the people behind them.